Showing posts with label snort. Show all posts

Wednesday, June 1, 2016

snort oinkmaster

To modify Signatures using oinkmaster.

modifysid 1000000 "\$EXTERNAL_NET" | "!\$HOME_NET"

modifysid 1000001 "\$EXTERNAL_NET" | "![10.0.0.1,10.0.0.2]"

modifysid 1000001 "\-> any" | "\-> ![10.0.0.1]"

disablesid 1000002

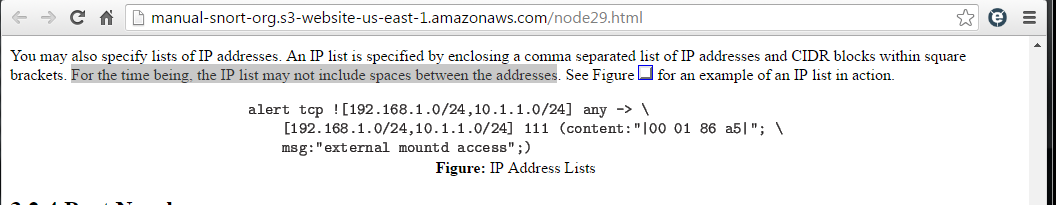
DANGER:  Don't you dare leave spaces between the IP address while you are negating them in modifysid shown in the second line.  The reference for that is shown below from snort manual.

Monday, June 9, 2014

Snort alert count on Google Earth

Requirement

For a long time I wanted to know how could I plot the alerts which each snort sensor is generating on a Google Earth based on geographic location.  If this could be done I could see from which location on the globe am I getting lots of alerts from.

Solution

The solution to my problem was all in the power of KML file.


Pre-requisites

1. Have snort running on many places.
2. Have barnyard to log your alerts (Optional if you are using old version of snort).
3. The last three characters of your sensors should be named after the airport code. (For example: Chennai sensor name "SensorMAA").  If you are wondering how to get all airport codes stick around.
4. View the snort generated alerts using BASE (Since my mysql query will work only on the BASE generated mysql schema).
5. Be able to run my bash script on the server which runs your mysql server.
6. Of-course Google Earth.

Making

Follow along there are a few steps.

1. Download the script and the support files as a zip from here.  The flow chart for creating the script is here.
2. Edit the file "GoogleEarth/Project/conf/mysql.cnf" to contain your IDS mysql credentials.
3. Run the file "GoogleEarth/Project/bash.sh" like ./bash.sh
4. Now Open the file "GoogleEarth/Project/Alerts.kml"
5. You could add bash.sh to a cron job which runs every 5 minutes so that the bar height on Google Earth would get updated automatically.


If you think I am forgetting something you bet your correct, you can get all the airport codes from the file you downloaded. "GoogleEarth/Project/resource/airport_codes.csv"


Sunday, August 11, 2013

IDS alert analysis

Today I was going through my IDS logs and found something suspicious.

The following are the steps I took to know that the alerts were benign.


I went inside the payload, nothing was evident.  So I wanted to know how did I end up on the IP 130.239.18.142, so I went to my proxy logs and grep'ed the IP.  In an instance I came to realize that I was downloading some ISO files.


Now to prove that the timing match,

The first field on the proxy logs is unix epoch time, I converted that (1374814496.635) using [date -d @1374814496.635 +"%d-%m-%Y %T %z"]  to verify the same. "26-07-2013 10:24:56 +0530"
The second field is the milliseconds which took to download the file "1330675". Since unix epoch time increments one per second I had to get the seconds component by dividing the number by 1000 which gives me approx 1330 and add this with the previous epoch time to get the TotalTime of 1374815826 which happens to translate to "26-07-2013 10:47:06 +0530"

This shows that the alerts were well within the time of the download and IDS was sure to trip off any data contained within the ISO file which is obviously falsepositive.  Case closed.

Tuesday, July 10, 2012

Analyzing a Snort Alert

Yesterday I was going about doing my things and suddenly noticed that there were three alerts on my IDS with the signature shown below.


I tried looking at the payload it was really huge like shown below.


I tried looking up the IP http://whois.domaintools.com/91.229.143.59 however I did not get any information useful to me.

I wanted to clean up the payload shown above to see just the URL, so I used the command as shown grep http tmp.txt | cut -d" " -f1 | grep \' | cut -d\' -f1


Well fair enough except the first one all the others does seem to be malicious, so I set out seeking my Web Proxy logs to see how did I land up on the IP.

One look at the proxy logs I almost felt like a amnesia patient getting back his\her memories :-D, because yesterday I was using urlquery.net for some experiment which I was performing. 


Bottom line: Long story short it really pays to have logging enabled to determine if an incident is a false positive or not :-)

Friday, March 16, 2012

Saturday, February 4, 2012

Snort Action

Snort can take the following types of Actions.


The Activate and Dynamic are dropped for the more recent Tagging and Flowbits

The actions of Drop, Reject and SDrop are used when Snort is in Inline mode.

Friday, January 27, 2012

Fixing SNORT BASE Graph with no legends

Wow after breaking my head for around 4 hours I did find a way to display information on the Graph which BASE produces.

The problem which I am facing is exactly described here.  http://seclists.org/snort/2011/q1/722 though the complete solution is not so here goes.


First we need to see what is the font which BASE is using.  That can be done by grepping for graph_font_name.

root@Bodhidarmar:/home/bala# grep graph_font_name /var/www/base/base_conf.php
        // $graph_font_name = "Verdana";
       $graph_font_name = "DejaVuSans";
        // $graph_font_name = "Image_Graph_Font";

Now that we found that BASE is going to user DejaVuSans fonts, we need to make sure that our system has that fonts.  If you cannot see them then copy these fonts from someother system and paste them in here.

root@Bodhidarmar:/var/www/base# ll /usr/share/fonts/dejavu/
-rw-r--r-- 1 bala bala 524056 2012-01-27 03:20 DejaVuSans-BoldOblique.ttf
-rw-r--r-- 1 bala bala 573136 2012-01-27 03:19 DejaVuSans-Bold.ttf
-rw-r--r-- 1 root root 301928 2009-08-27 19:56 DejaVuSansMono-Bold.ttf
-rw-r--r-- 1 root root 321524 2009-08-27 19:56 DejaVuSansMono.ttf
-rw-r--r-- 1 bala bala 523804 2012-01-27 03:20 DejaVuSans-Oblique.ttf
-rw-r--r-- 1 bala bala 622280 2012-01-27 03:19 DejaVuSans.ttf
-rw-r--r-- 1 root root 306532 2009-08-27 19:56 DejaVuSerif-Bold.ttf
-rw-r--r-- 1 root root 328908 2009-08-27 19:56 DejaVuSerif.ttf

root@Bodhidarmar:/var/www/base#

Now this is the part which made me run mad,  this site came to my rescue https://help.ubuntu.com/community/PhpPear , I just need to have a soft link of the font being used inside the PHP directory.

root@Bodhidarmar:/usr/share/php/Image/Canvas# ln -s /usr/share/fonts/truetype/ttf-dejavu/ Fonts
root@Bodhidarmar:/usr/share/php/Image/Canvas# ll
-rw-r--r-- 1 root root  6604 2012-01-27 03:54 Color.php
lrwxrwxrwx 1 root root    37 2012-01-27 04:12 Fonts -> /usr/share/fonts/truetype/ttf-dejavu//

Thursday, January 19, 2012

SNORT MYSQL

Here I have shown how to prepare mysql to work with Snort.  Assuming mysql is already installed.
 
root@snortbox:/store/snort/src/snort-2.9.1# mysql -u root -p
Enter password:
mysql> show databases;
+---------------------------------+
| Database                     |
+---------------------------------+
| information_schema     |
| mysql                         |
+---------------------------------+

2 rows in set (0.01 sec)
Now let us create the MySQL database and tables in order to receive the Snort logs:
mysql> create database snort;
Query OK, 1 row affected (0.01 sec) Since it is dangerous to access the database with the root user, we need to create a user who has only permissions on the snort database:
mysql> grant all on snort.* to snortuser@localhost identified by 'snortpassword';
Query OK, 0 rows affected (0.01 sec)
Now to reload mysql privileges.
mysql> flush privileges;
Query OK, 0 rows affected (0.01 sec)
mysql> exit;
Bye
Now we will import the mysql schema which snort knows to use.
root@snortbox:/store/snort/src/snort-2.9.1/schemas# ls
create_db2    create_mysql       create_postgresql  Makefile.am
create_mssql  create_oracle.sql  Makefile           Makefile.in
root@snortbox:/store/snort/src/snort-2.9.1/schemas# mkdir /usr/share/doc/snort-mysql/
root@snortbox:/store/snort/src/snort-2.9.1/schemas# cp create_mysql /usr/share/doc/snort-mysql/
Manual installation
#mysql -u root -p snort < schemas/create_mysql

Tuesday, January 17, 2012

Sudo echo does not work :-0

Today I found the hard way that sudo echo will not work in Ubuntu and a good explanation is given here

http://blogs.oracle.com/joshis/entry/sudo_echo_does_not_work

Here is a small script I use to start a VM and point the system to use the VM as gateway to the internet :-)

bala@lapi:~$ cat ./Go_through_SNORT.sh
#!/bin/bash
#Author: Balasubramaniam Natarajan
#Date: 13-Dec-2011
#This script will set the default route to Bodhidarmar
# and will add in the name server
VBoxManage startvm SNORT
sudo route add default gw 192.168.56.101
sudo sh -c 'echo "nameserver 192.168.1.1" >> /etc/resolv
bala@lapi:~$

Monday, January 16, 2012

Snort's Classfication.config

Here you can see that I have arranged the snort rule classification in ascending to descending order.
 
bala@Bodhidarmar:/store/snort/etc$ cat classification.config | grep "config classification: " | sort -t"," -k3
config classification: attempted-admin,Attempted Administrator Privilege Gain,1
config classification: attempted-user,Attempted User Privilege Gain,1
config classification: inappropriate-content,Inappropriate Content was Detected,1
config classification: policy-violation,Potential Corporate Privacy Violation,1
config classification: shellcode-detect,Executable Code was Detected,1
config classification: successful-admin,Successful Administrator Privilege Gain,1
config classification: successful-user,Successful User Privilege Gain,1
config classification: unsuccessful-user,Unsuccessful User Privilege Gain,1
config classification: web-application-attack,Web Application Attack,1
config classification: trojan-activity,A Network Trojan was Detected, 1
config classification: attempted-dos,Attempted Denial of Service,2
config classification: attempted-recon,Attempted Information Leak,2
config classification: default-login-attempt,Attempt to Login By a Default Username and Password,2
config classification: denial-of-service,Detection of a Denial of Service Attack,2
config classification: misc-attack,Misc Attack,2
config classification: non-standard-protocol,Detection of a Non-Standard Protocol or Event,2
config classification: rpc-portmap-decode,Decode of an RPC Query,2
config classification: sdf,Sensitive Data was Transmitted Across the Network,2
config classification: successful-dos,Denial of Service,2
config classification: successful-recon-largescale,Large Scale Information Leak,2
config classification: successful-recon-limited,Information Leak,2
config classification: suspicious-filename-detect,A Suspicious Filename was Detected,2
config classification: suspicious-login,An Attempted Login Using a Suspicious Username was Detected,2
config classification: system-call-detect,A System Call was Detected,2
config classification: unusual-client-port-connection,A Client was Using an Unusual Port,2
config classification: web-application-activity,Access to a Potentially Vulnerable Web Application,2
config classification: bad-unknown,Potentially Bad Traffic, 2
config classification: icmp-event,Generic ICMP event,3
config classification: misc-activity,Misc activity,3
config classification: network-scan,Detection of a Network Scan,3
config classification: not-suspicious,Not Suspicious Traffic,3
config classification: protocol-command-decode,Generic Protocol Command Decode,3
config classification: string-detect,A Suspicious String was Detected,3
config classification: unknown,Unknown Traffic,3
config classification: tcp-connection,A TCP Connection was Detected,4
bala@Bodhidarmar:/store/snort/etc$
Saturday, January 14, 2012

Writing SNORT Rules :-D

Follow these simple steps to write a snort rule.


After writing the second row in a notepad, save it as streamingvideo.rules and we have to include it in the snort config file along with other rules.

Wola that is it, we have created our first snort rule :-)

Monday, December 12, 2011

SNORT Sig updates Including SED

Whenever I update Snort Rules, the five SID mentioned below gets additional ! before $DNS server which makes SNORT not to start.  All these SID are included inside emerging-current_events.rules.

sid:2013353
sid:2013354
sid:2013355
sid:2013358
sid:2013359

so as a work around I have included sed "Serial Editor" along with my snort rules update script as shown below.

root@Bodhidarmar:/store/snort/rules# cat /var/scripts/snort_update.sh

#!/bin/bash
wget -q http://www.snort.org/sub-rules/snortrules-snapshot-xxxx.tar.gz/aaabbbcccdddeeefffggghhhiiijjjkkk -O /store/snort/archive/snortrules-snapshot-xxxx.tar.gz
oinkmaster.pl -o /store/snort/rules/ -Q
echo "Now Running Serial Edit to change the Bang Dollar DNS to Dollar DNS in ET-current_event[DOT]rules"
sed s/\!\$DNS/$DNS/ /store/snort/rules/emerging-current_events.rules > /store/snort/rules/emerging-current_events.rules


Note I have reduced the Font size above as they needs to be on one single line.

Saturday, December 10, 2011

Snort Sensor Name

To get the name of the sensor which is logging a particular event we need to include  sensor_name=Bodhidarmar in the snort.conf file.


root@Bodhidarmar:/home/bala# grep sensor_name /etc/snort/snort.conf
output database: log, mysql, user=********** password=**************** dbnames=******* host=localhost sensor_name=Bodhidarmar

Thursday, December 8, 2011

Snort - fixing Error PortVar Lookup failed on '$FILE_DATA_PORTS'.

When we get the error "PortVar Lookup failed on '$FILE_DATA_PORTS'." on starting SNORT, this means to say that we need to declare the ports for '$FILE_DATA_PORTS' in our snort.conf file.


Source


http://blog.joelesler.net/

http://vrt-blog.snort.org/2011/11/say-hello-to-file-identify-category.html

SNORT FQDN resolution

If we want BASE to do resolution of the IP addresses as shown below.


We need to edit base_config.php file under the document root.


Tuesday, November 22, 2011

Snort mysql compilation

http://www.mcabee.org/lists/snort-users/Jan-04/msg00497.html
make distclean
The command shown above make the trick for me to get my snort to compile successfully with mysql :-)

Sunday, August 21, 2011

Snort libdnet

http://forums.snort.org/forums/snort-newbies/topics/libdnet-not-found

whereis libdnet

LD_LIBRARY_PATH=/usr/local/lib
export LD_LIBRARY_PATH

Saturday, August 13, 2011